Teasing out the questions around construction third-party risk management
In the previous article, we have touched on the increasingly complex business environment where cost and risk have their intricate dance.
Today, let’s tease out a few more aspects of third party risk management.
The supply chain uniqueness of asset builders, owners, and managers
“In Australia, subcontractors are responsible for between 80 per cent and 85 per cent of all construction work, the highest involvement of subcontracting in the world.”
This “pyramid of contractual relationships” is also prevalent among industries such as Forestry, Mining and Energy.
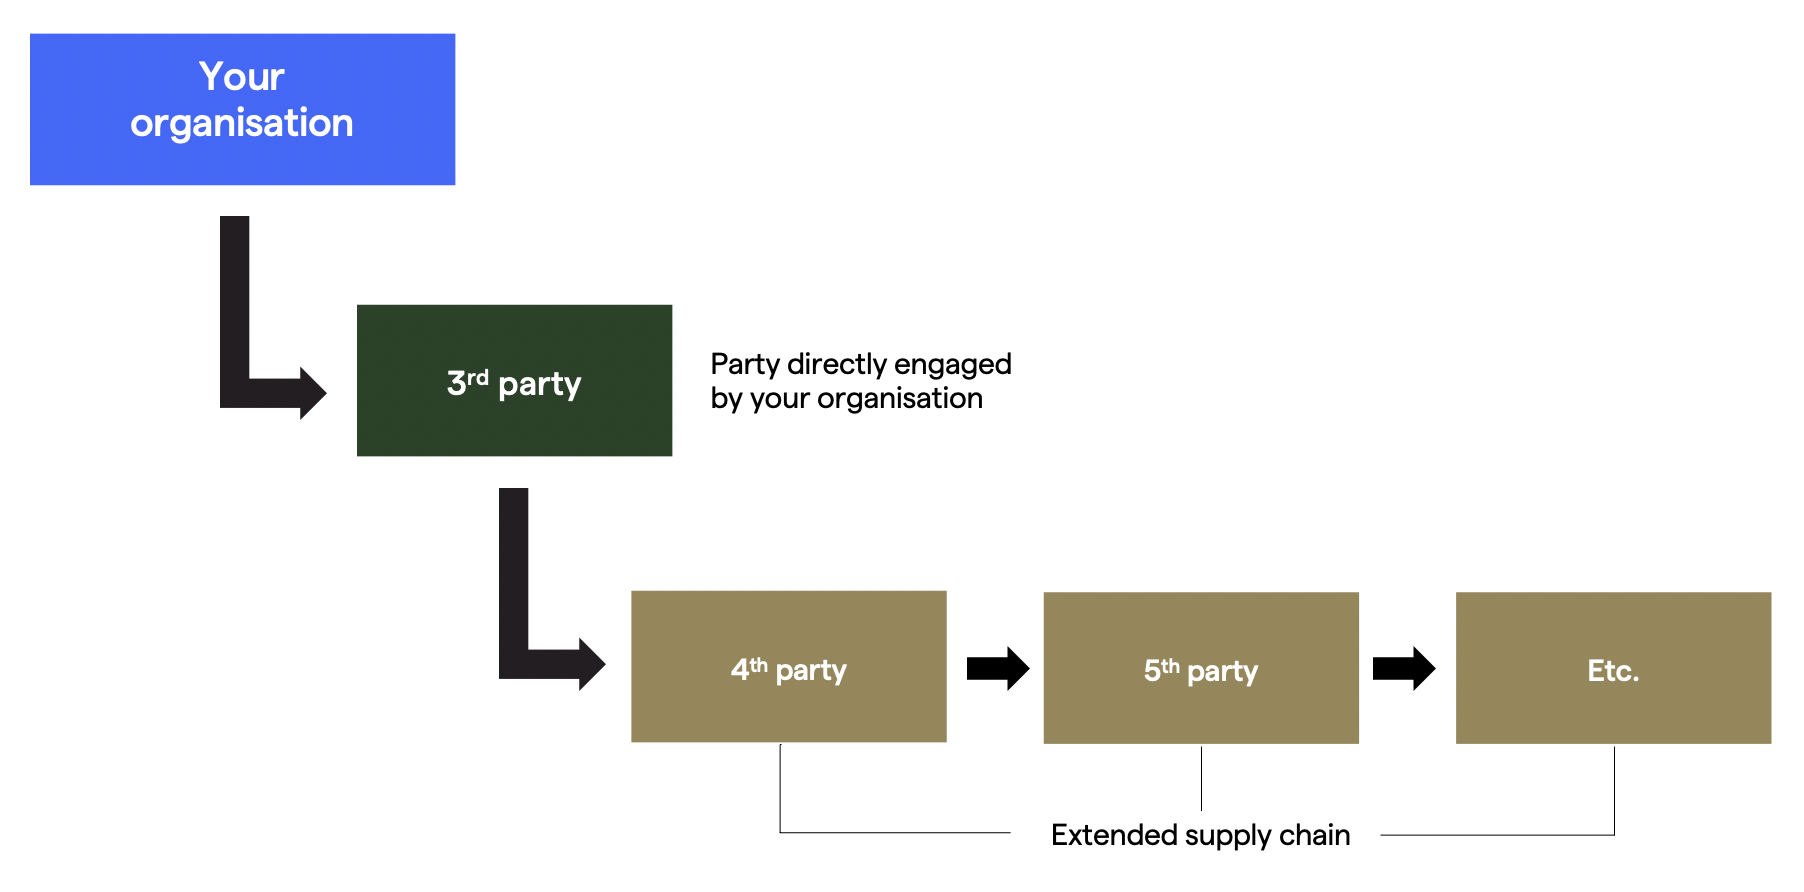
As mentioned in the previous article, the business environment is getting more complex. As projects get bigger, the number of parties increase, leading to an equal increase of contracts, and indeed an increase in supply chain complexity.
Imagine how complicated the above diagram would be if your organisation has 500, 1000, or 10000 vendors.
| Mini question: Do you have visibility into all third parties? What about the extended supply chain? |
Back to basics with risk and consequences
The common adage is “great risk great return.” There are indeed some risks worth taking as companies stand to gain from cost efficiency and external expertise. However, organisations need to understand their risk appetite – which is the “type and extent of risk that an organisation is willing to accept in its pursuit of value.”
Let’s take a step back and hone in on the basics.
There are two ways to look at risks: internally influenced (e.g. company policies, management ethos) and externally influenced. Both can be equally serious, even though you often hear about external risks more in the news (e.g. recession, natural disasters).
What are the adverse consequences of risk? They fall under three broad categories: operational, financial and reputational.
| Operational examples | Financial examples | Reputational examples |
|
|
|
Types of risk consequences and examples. Adapted from the CIPS Resilience Model.
These consequences are often interlinked.
For instance, since COVID-19 officially became a pandemic, more than half (51%) of organisations faced one or more third-party risk incident. These tend to have more operational and financial impacts.
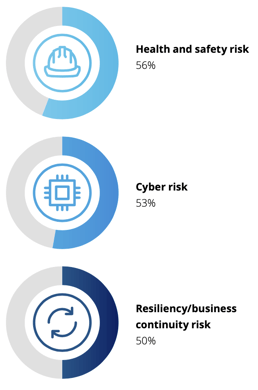 Risk domains most likely to be affected during the pandemic. Source: Deloitte
Linking financial and reputational consequences, earlier academic research has confirmed that regulatory punishment “causes shareholder losses that are, on average, 10 times the size of the penalty itself and negatively impacts share prices, on an average by around 2.55% in the three days after the announcement, where direct harm to customers and investors is involved.”
Mini questions:
|
“It’s your problem not mine” is no more
Vendor risk assessment has traditionally been performed at the beginning of a new relationship. Once a new contract is signed, there is little, if any, ongoing risk assessment as long as no serious incident occurs. Because this vendor prequalification process is typically a single event triggered by the onboarding of a new vendor, it is viewed as a procurement process.
However, who “works in procurement” is different to “who does procurement.” Given the changing operating models of procurement, the blurring of lines can cause a diffusion of accountability.
Good vs bad
So what are some other characteristics of an immature third-party risk management program?
- Siloed or domain-specific approach
- Lacking or confusing measurements of success
- Reactive to legislation with no long-term integrated plan
- Investment not being put to good use or underinvestment
In contrast, what does good look like?
- “Most leaders have a formal and structured Supplier Relationship Management (SRM) program in place, compared to more than 50% of other companies, which have only an ad hoc approach to SRM. Furthermore, 70% of leaders have differentiated programs for strategic and mainstream suppliers, compared to less than 5% of others.”
- Clear owners of ultimate responsibility and budget, even though the two can be different groups
- Integrated infrastructure to support processes that are aligned with best practices
- And elements like in the diagram below:
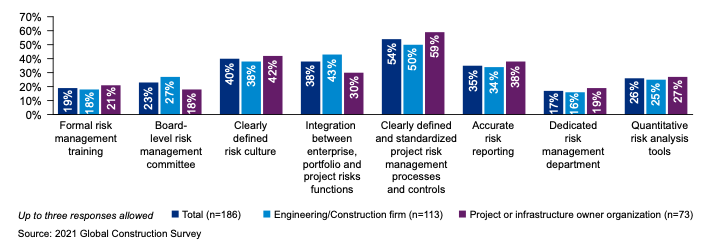 Source: KPMG
Ask and you shall find the answer
Without needing a full-blown assessment framework, just ask yourself a few questions:
|
If you are interested in understanding where your organisation is, how the industry is doing, and how to improve your third-party risk management play, check out our upcoming research paper "Building in the Dark - High-risk Supply Chains: Attitudes, Responses & Opportunities."
It’s specifically relevant for those who rely heavily on services focused supply chains, often with a high concentration of high-risk subcontractors.
Recent Articles
Contractor prequalification: What to check before you sign a vendor
Bringing on a new contractor always carries some risk. Will they deliver on time? Are they financially stable? Do they carry the right insurance? Contractor prequalification is how procurement teams answer those questions before a contract is signed, rather than finding out the hard way mid-project.

Vendor onboarding vs prequalification: what’s the difference, and why it matters
Ask most procurement teams if their vendors are onboarded, the answer is yes. Ask if they are prequalified, and the answer gets a lot less certain. That gap – between having a vendor’s details and knowing who you’re working with – is where a lot of supply chain risk quietly lives.

Top 10 procurement best practices to implement immediately
Procurement teams are under increasing pressure to control costs, reduce risk, maintain compliance, and keep operations moving efficiently. At the same time, stakeholders expect faster decisions, better supplier visibility, and stronger governance across the purchasing process.